Compliance
Published on
SOC 2 and GDPR feedback workflow
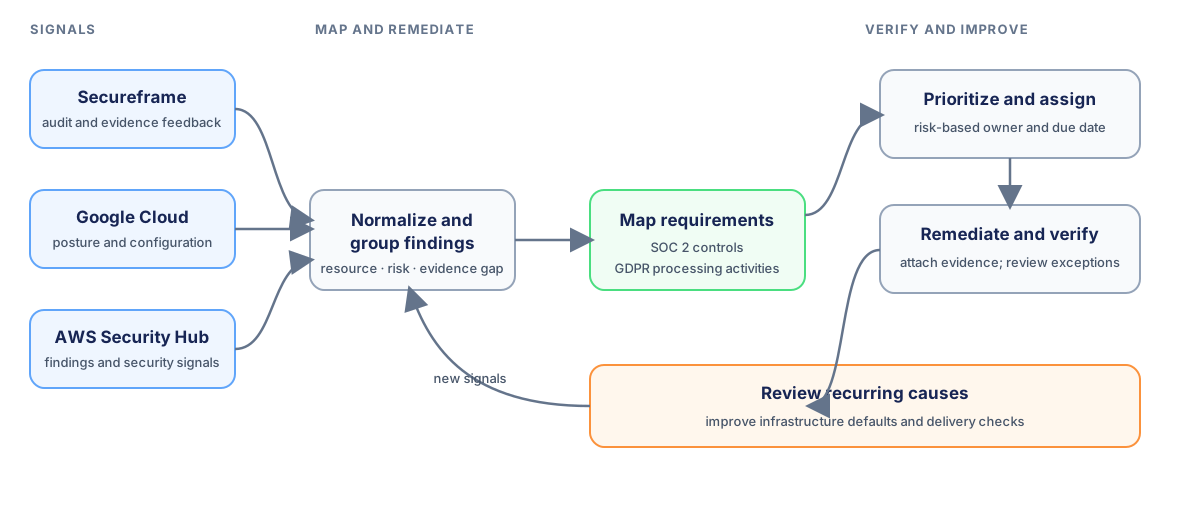
Use compliance feedback as input to a repeatable engineering loop. Normalize audit and cloud findings, map each issue to the relevant control or data processing activity, then assign and verify remediation.
Turn feedback into owned work
Use Secureframe feedback to identify evidence gaps, unclear control ownership, and recurring exceptions. Correlate those themes with cloud posture and detection feedback from Google Cloud Platform and AWS Security Hub. For each finding, capture the affected resource, risk, control or requirement, owner, remediation, and evidence needed to verify closure.
Prioritize exposed or high-impact issues first. Automate repeatable checks where practical, and route exceptions through a documented risk owner, compensating controls, and expiry.
Keep evidence tied to the requirement
For SOC 2, connect evidence to the control and audit period in scope, with a clear operational owner. For GDPR, connect findings to the data and processing activity involved, access boundaries, retention, and the response path.
Treat Secureframe and cloud tools as sources of signals and evidence. Confirm applicability and closure with the control owner instead of treating a dashboard status as proof by itself. Review recurring causes with engineering and compliance stakeholders, then feed those patterns into infrastructure defaults and delivery checks.